Cloning for ServiceNow
Take control of clone operations before they take control of you
Every clone resets your audit trail, disrupts work in progress, and creates environment drift that takes days to reconcile. xtype gives platform teams full clone lifecycle management, from pre-clone preview through post-clone restore, so cloning becomes a governed, predictable event rather than a source of chaos.



Stop letting clone operations derail your ServiceNow delivery
Most teams treat cloning as an unavoidable disruption. xtype makes it a controlled, automated event with no surprises and no manual scramble.
The current way
 Broken authorization chainEvery clone resets the change history of the
target instance, erasing the evidence of who changed what and breaking the authorization
chain regulators require.- Admin access is the price of movementClone operations require elevated access across environment boundaries. Work in progress is lost, restore plans live in spreadsheets, and the same manual process repeats every cycle.
- Audits are reconstruction projectsClone events wipe the audit trail within the
cloned instance. Evidence has to be assembled from disconnected sources after the fact, weeks behind delivery.
With

 OBSERVE: One authoritative viewEvery change, access decision, and
configuration visible across every instance
through every clone-down in real time. Authorization chain preserved. Nothing reset.- CONTROL: Policy enforced at runtimeAutomated, policy-driven clone lifecycle management from preview through post-clone restore. Developers operate without admin access. Every restore executed from an immutable, automated runbook.
- PROVE: Compliance is always onImmutable audit logs that survive every clone and upgrade. Compliance evidence aligned to SOX, HIPAA, DORA, NIS 2, and GxP produced automatically. Audits become a query, not a project.
Switch to security that’s enforced at runtime, not documented after the fact
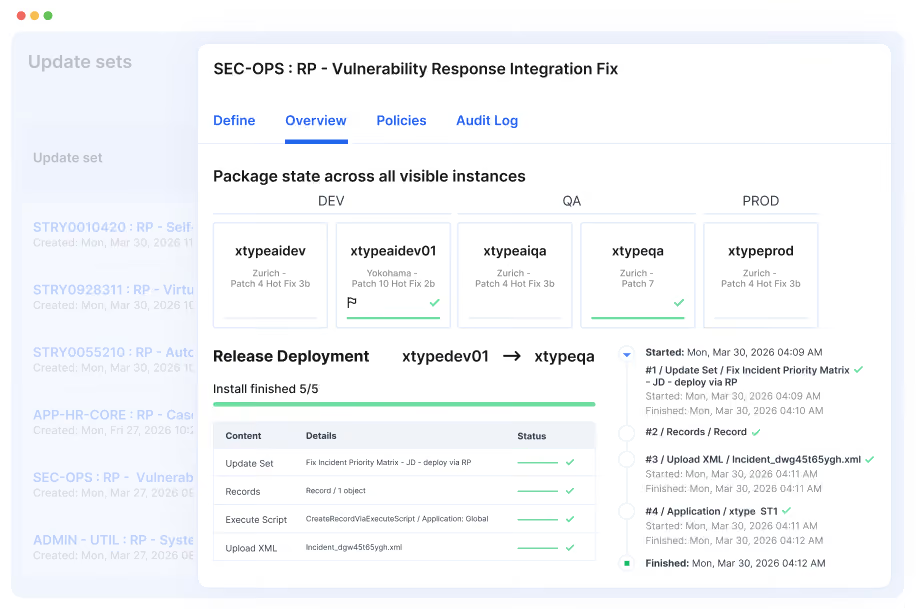
Observe
Full visibility into every environment before, during, and after every clone
- Live comparison of source and target instances before
any clone executes - Inconsistencies in update sets, apps, and plugins
surfaced automatically - Configuration drift detected in real time across every instance in the estate
- Iterative snapshot tracking throughout the pre-clone process
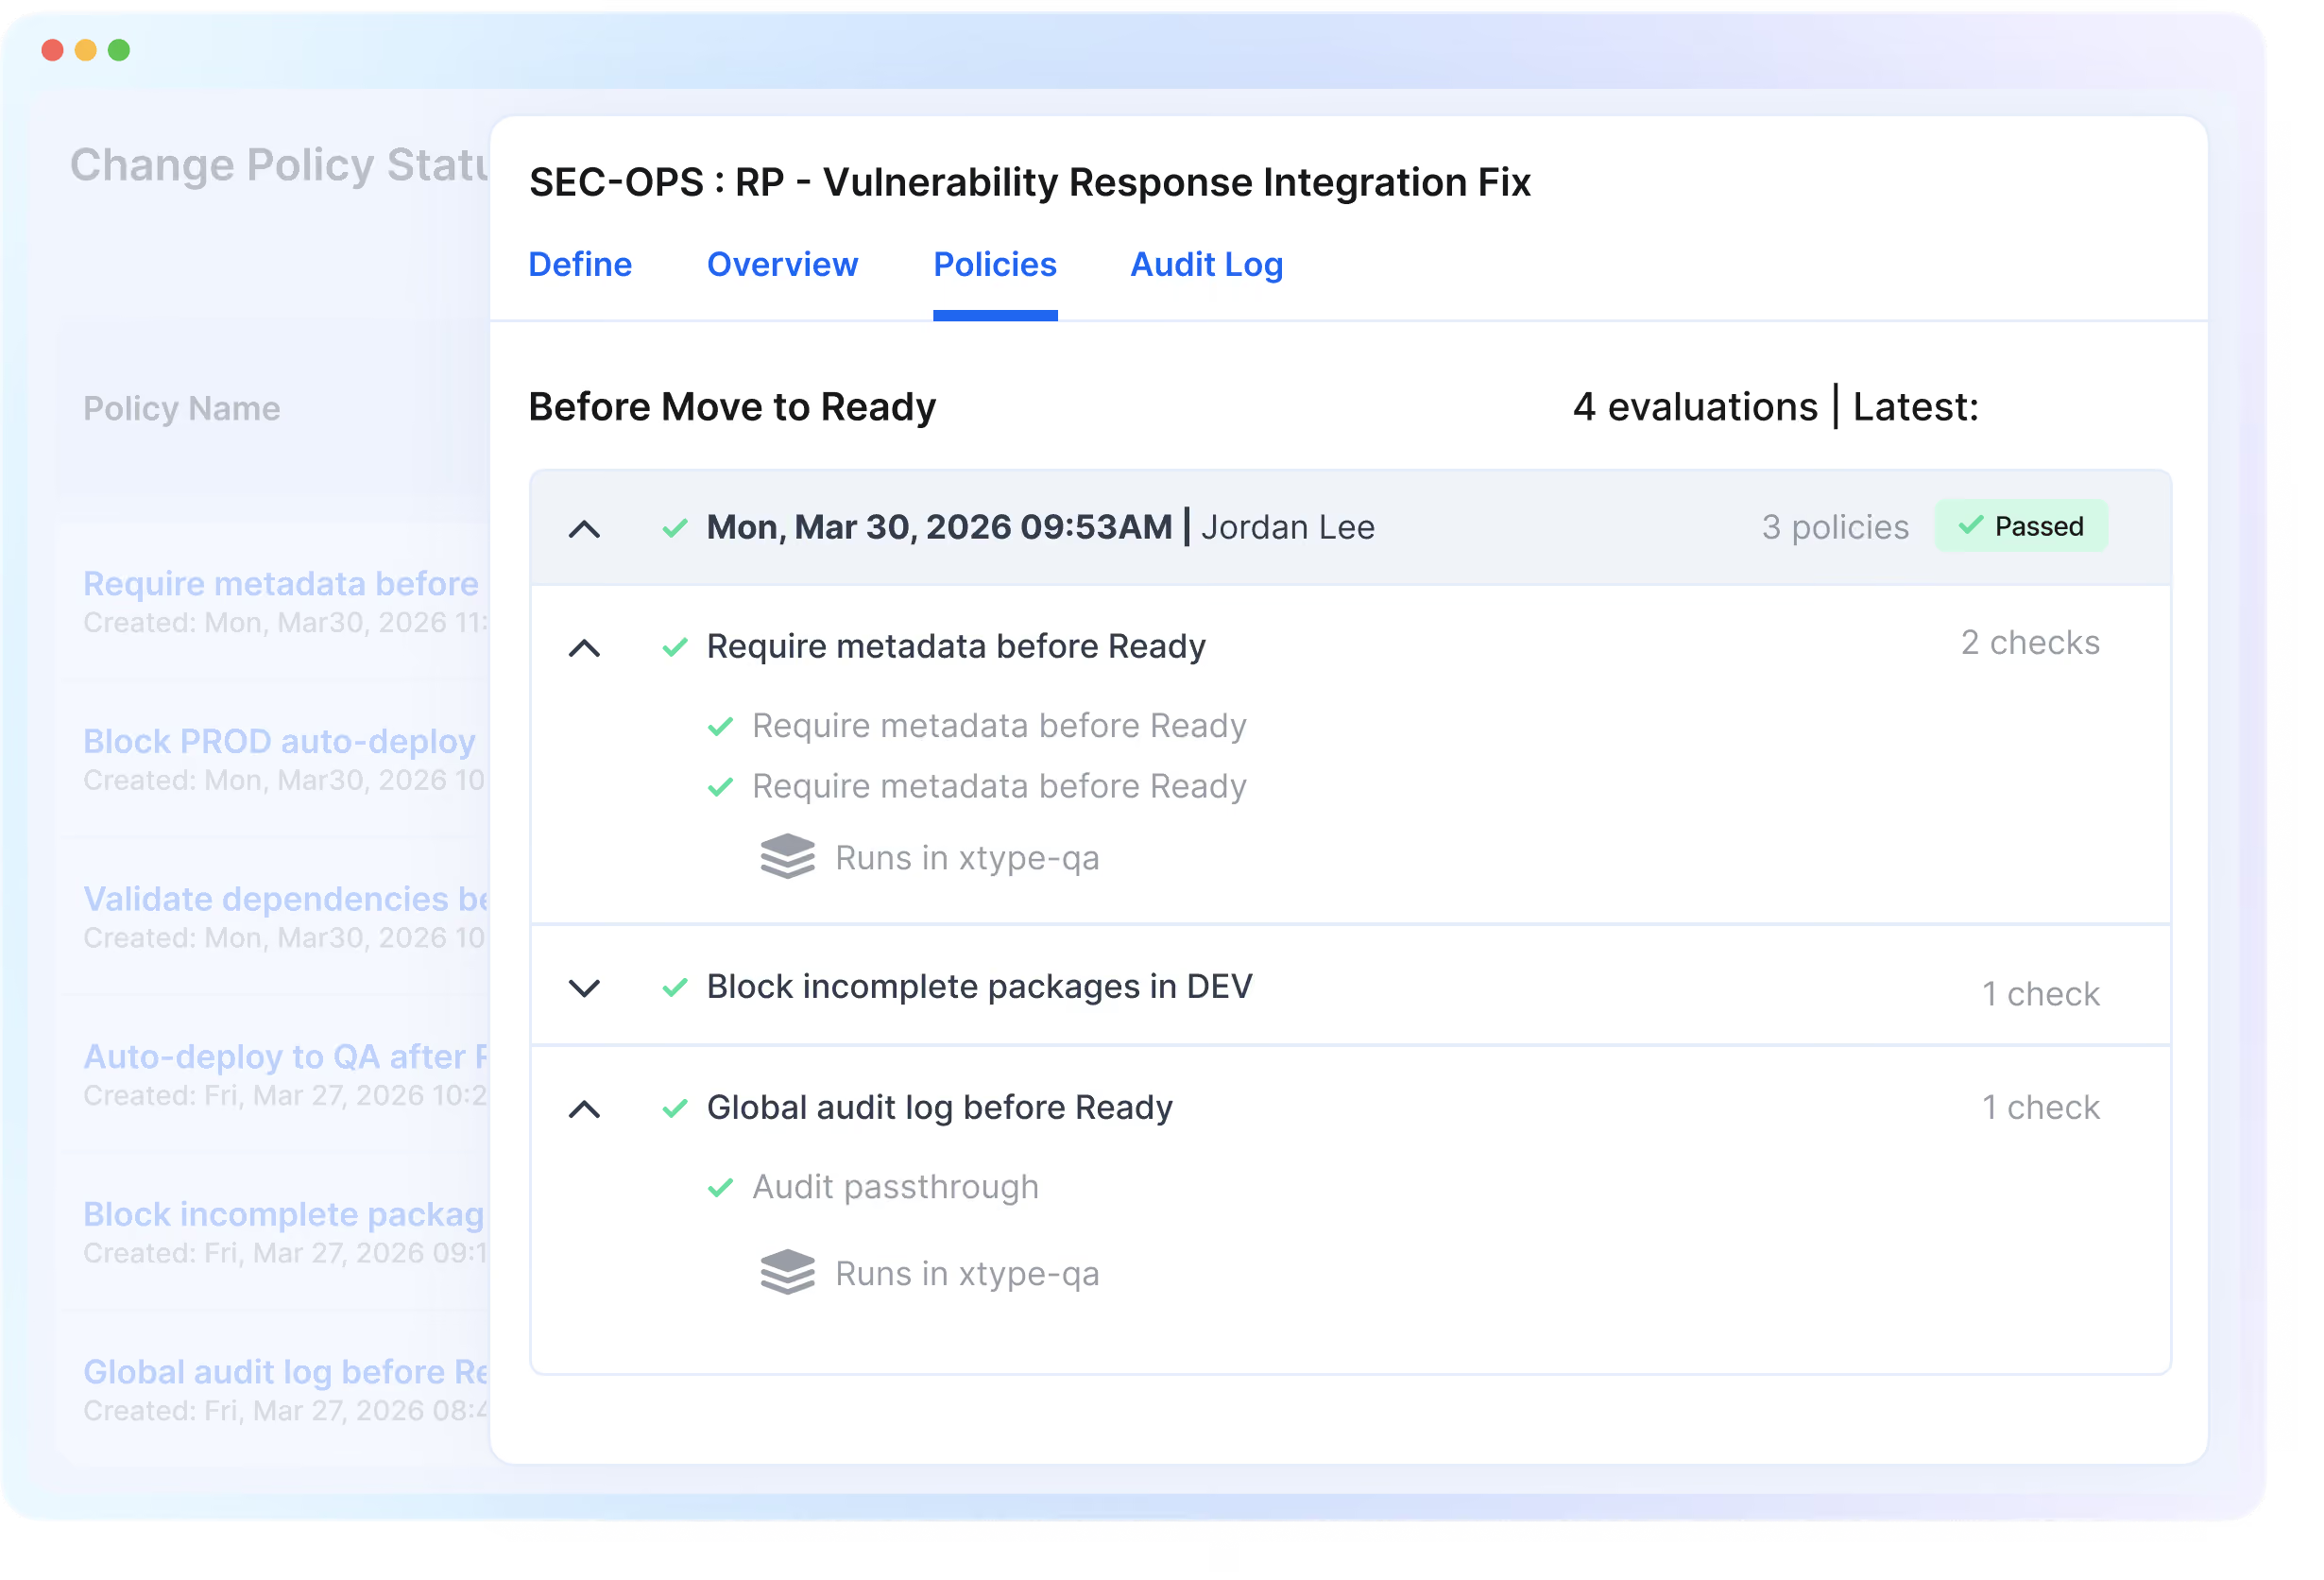
Control
Automated clone lifecycle management that removes the manual overhead entirely
- Pre-clone preview identifies every inconsistency before
the operation runs - Automated backup runbooks generated and executed without manual effort
- Work in progress captured and restored automatically
after every clone - Package-based restore synchronized across all
cloned instances - Shareable clone plans keep every stakeholder aligned
before execution
PROVE
Immutable records that survive every clone and make compliance continuous
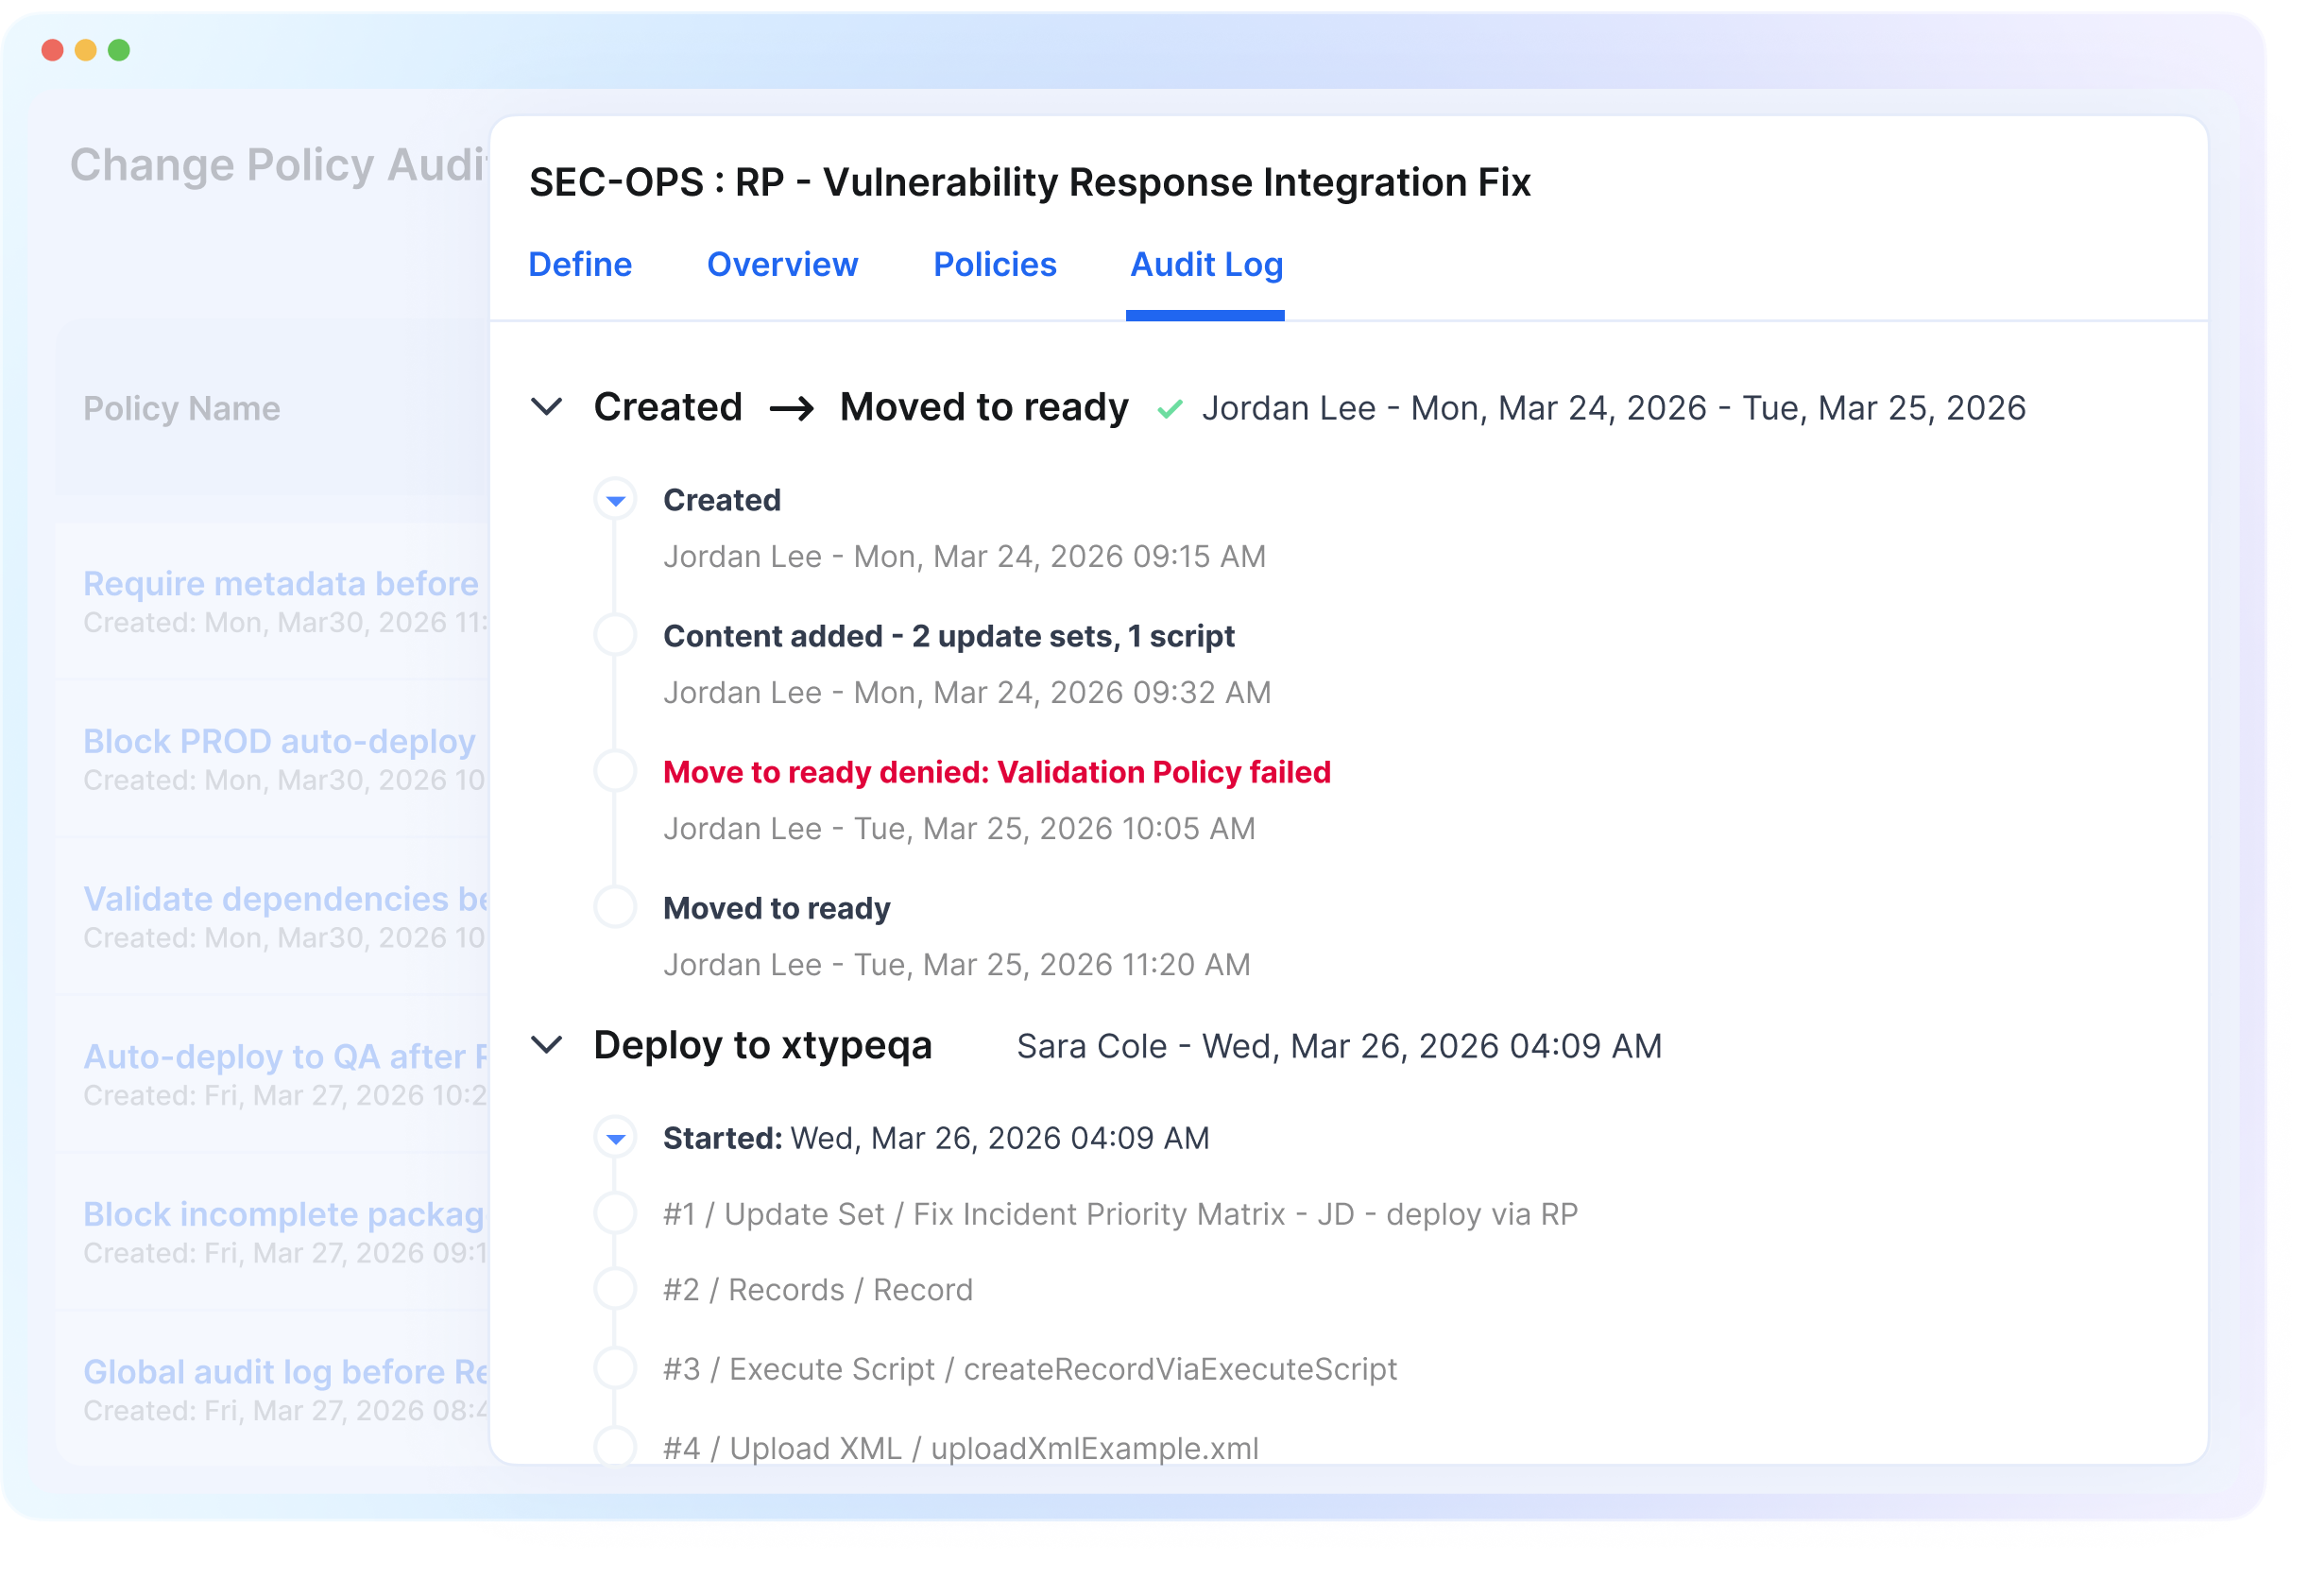
- Tamper-proof audit trails preserved through every clone operation and upgrade
- Full authorization chain maintained across every environment boundary
- Alignment to SOX, HIPAA, DORA, NIS 2, and GxP always on
- When auditors ask for evidence, it is already there
Move faster and more securely with governed clone operations

No more work in progress lost to cloning
xtype captures and restores work in progress automatically after every clone event. What used
to cost developers 8 to 10 hours per clone cycle becomes a non-event.
to cost developers 8 to 10 hours per clone cycle becomes a non-event.

Accurate clones that reduce post-clone troubleshooting
Pre-clone environment comparison surfaces every inconsistency before the operation runs. Fewer surprises. Less rework. More time delivering.

Compliance records that survive
every clone
xtype audit logs exist outside the cloned instance and are tamper-proof. Clone events never reset
your compliance record. The full history is always intact and available on demand.
your compliance record. The full history is always intact and available on demand.

Discover how to
eliminate clone disruption in ServiceNow
Explore our ServiceNow case studies to see the latest trends, insights, best practices, and everything in between.
Eliminate privilege sprawl and enforce separation of duties across your ServiceNow estate
See how xtype enforces access controls, eliminates privilege sprawl, and creates a tamper-proof record of every change across your ServiceNow estate.
- Explore the platform and see it in action.
- See how xtype integrates with your ServiceNow environment.
- No commitment - just a chance to get your questions answered.
Frequently asked questions
How does xtype enforce least privilege across ServiceNow environments?
xtype replaces the need for admin access at environment boundaries with policy-enforced deployment pipelines. Developers deploy through xtype using stage-specific permissions scoped to their role. Elevated credentials are never required, and access is technically enforced rather than procedurally assumed.
Can xtype enforce separation of duties natively in ServiceNow?
Yes. xtype enforces SoD at the platform level through granular RBAC with stage-specific permissions. The same user cannot write, approve, and deploy a change to production. This is enforced technically by xtype, not documented in a policy that relies on people following the right process.
What happens to access records during a ServiceNow clone operation?
xtype maintains immutable audit trails that survive clone operations and upgrades. The full authorization chain, including who had access to what and when, is preserved outside the cloned instance, so clone events do not reset or break your security record.
Does xtype extract or store ServiceNow data outside the platform?
No. xtype is built natively inside every ServiceNow environment. It operates entirely within the platform's own security model. No data is extracted, copied, or exposed externally. This is what makes xtype ServiceNow Store certified and trusted by auditors.
How does xtype detect and remediate permission drift?
xtype continuously monitors role and entitlement state across every instance in your estate. When drift is detected, such as a role accumulating privileges beyond its intended scope or a stale permission persisting after a clone, xtype surfaces it in real time and can trigger automated remediation.